
Cybersecurity
The Managed Cybersecurity Lifecycle
Almost every organization we assess has already bought good security controls. Rather fewer are still operating them as designed a year later. The gap between those two sentences is what managed cybersecurity exists to c...
What Are Managed Cybersecurity Services?
Managed cybersecurity services are the continuing operation of an organization's security controls by somebody whose job that is. Not the purchase of the controls, and not a one off review of them. The operation: the pat...

Cybersecurity Risk Assessments
A cybersecurity risk assessment answers one question: what could go wrong here that would matter, and which of those things is worth spending money on first. Everything else in the method exists to make that answer defen...

Vulnerability Management
Vulnerability management is the discipline of finding weaknesses in your environment and closing them before somebody else uses them. Almost every organization does the finding. Rather fewer do the closing at a rate that...
Security Monitoring and Incident Detection
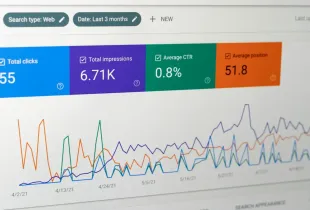
Security monitoring is the practice of collecting enough evidence about what is happening in an environment to notice when something is wrong, and having somebody act on it. Both halves are load bearing. Organizations th...

Incident Response and Cybersecurity Recovery
Incident response is the set of activities that begin when something has gone wrong and end when the organization is back to a state it understands. It is the part of a security program that is dormant until it is the on...
Security Hardening and Configuration Management
Hardening is the practice of reducing what a system can do to the set of things it needs to do. Configuration management is the practice of keeping it that way. The first is a project and is routinely completed. The seco...

Identity and Access Management
Identity is the control surface that matters most, because most intrusions are not break ins. They are logins. An attacker with a valid credential does not need an exploit, is difficult to distinguish from a user, and in...
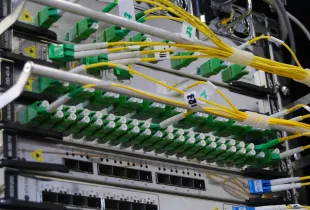
Network Security
Network security used to be a question of drawing a line and defending it. That model has not disappeared, but it has stopped being sufficient, and the organizations in the most difficulty are usually the ones still oper...
Endpoint and Server Security
Endpoints are where most intrusions become real. A phishing message is delivered somewhere, a credential is used somewhere, and a payload runs somewhere, and that somewhere is almost always a workstation or a server. It ...