
IT Governance
Develop comprehensive IT governance frameworks that balance innovation, regulatory compliance & operational control while aligning with business goals.

Cloud Cost Optimization and FinOps
Cloud bills grow because cloud makes provisioning easy and de-provisioning optional. Nothing forces the conversation that a purchase order used to force, so capacity accumulates quietly and the total becomes a surprise s...

Government and Public-Sector Cloud Infrastructure
Public-sector infrastructure decisions are made under constraints that commercial organizations do not share. The technology is the same; the authorization, procurement, records and transparency obligations around it are...
The Managed Cybersecurity Lifecycle
Almost every organization we assess has already bought good security controls. Rather fewer are still operating them as designed a year later. The gap between those two sentences is what managed cybersecurity exists to c...

Cybersecurity Risk Assessments
A cybersecurity risk assessment answers one question: what could go wrong here that would matter, and which of those things is worth spending money on first. Everything else in the method exists to make that answer defen...

Identity and Access Management
Identity is the control surface that matters most, because most intrusions are not break ins. They are logins. An attacker with a valid credential does not need an exploit, is difficult to distinguish from a user, and in...
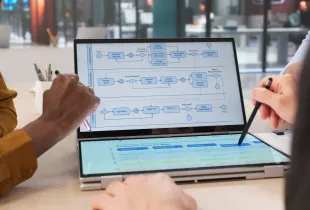
The CIS Critical Security Controls
Most security frameworks tell you what good looks like. Very few tell you what to do on Monday. The CIS Critical Security Controls are an attempt at the second problem, and that is the reason to be interested in them.
Th...
Cybersecurity Policies and Documentation
Security documentation has a reputation problem. It is associated with binders written for an audit, approved once, and never read again. That reputation is deserved for a great deal of it, and it obscures the fact that ...
Continuous Security and Compliance Monitoring
Passing an assessment and maintaining an effective security program are different achievements, and the second is considerably harder. An assessment measures a moment. A program has to hold a position while the environme...
The NIST Cybersecurity Framework
The NIST Cybersecurity Framework is the most widely used way of organizing a conversation about cybersecurity risk, and it is regularly misdescribed. It is not a standard, not a control catalog, and not something an orga...
NIST SP 800-53 Security Controls
NIST SP 800-53 is a catalog of security and privacy controls. It is thorough, it is long, and it is routinely misunderstood as a list an organization is supposed to complete. It is not, and reading it that way produces e...