
Solution Brief
Cybersecurity Compliance & Audit Readiness
When a contract, regulator or customer asks you to demonstrate security, LABUSA shows where you stand, what the gaps are and what closing them will take.
LABUSA assesses your security controls against the specific contract, regulation or standard you must meet, identifies the gaps and builds a remediation plan you can cost and carry out. LABUSA prepares you for formal audits. It is not a certification body or an independent auditor.
Solution highlights
-
Security Assessments
Controls reviewed on evidence against the requirement you have been asked to meet.
-
Control Alignment
Practice aligned with NIST, CIS or ISO/IEC 27001 where your obligation applies.
-
Compliance Preparation
Evidence organized and ready before the formal assessment begins.
-
Remediation Planning
Every gap sequenced and costed so it can be funded and fixed.
How it works
Solution at a glance
Text description of this infographic
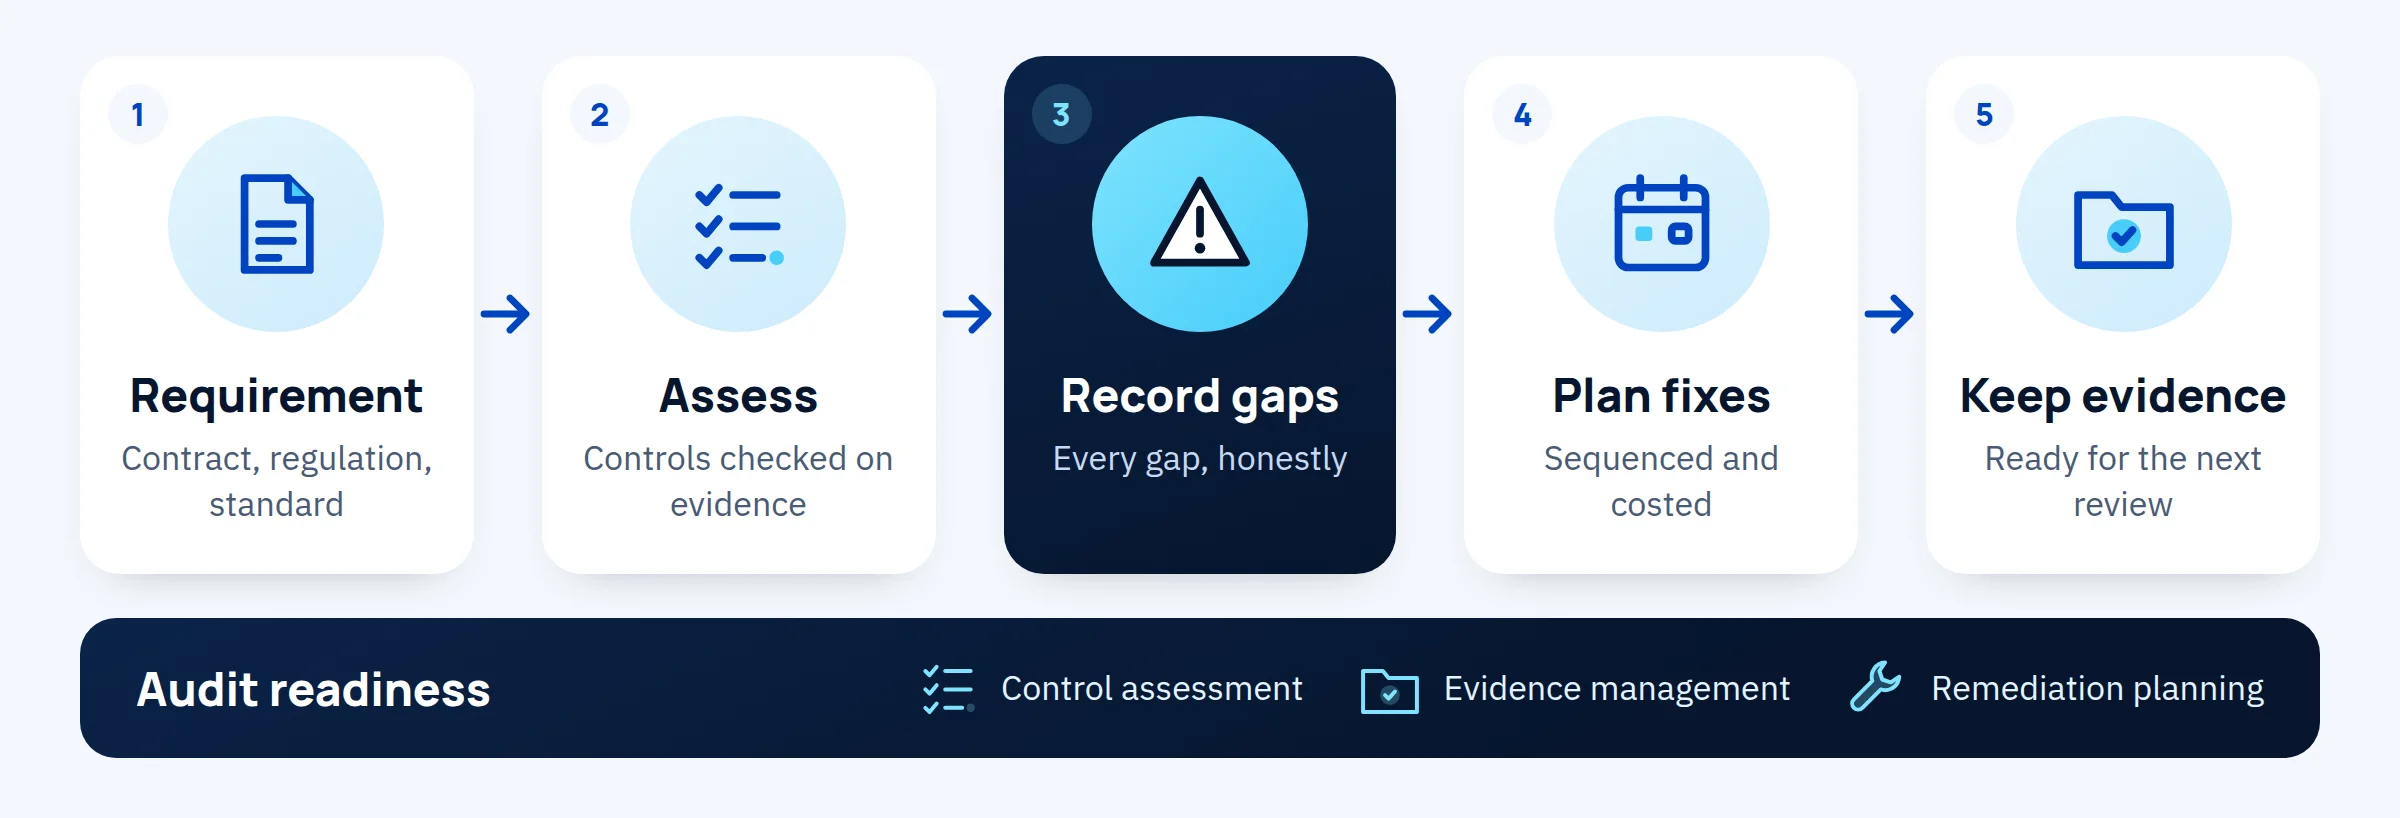
A five-step workflow, read left to right. First, Requirement: contract, regulation, standard. Second, Assess: controls checked on evidence. Third, Record gaps: every gap, honestly. This step is highlighted as the point where people decide. Fourth, Plan fixes: sequenced and costed. Fifth, Keep evidence: ready for the next review. Underneath, Audit readiness: control assessment, evidence management and remediation planning.
The Business Challenge
Compliance shouldn't be a scramble before every deadline.
Compliance is often treated as a deadline rather than an ongoing program. The same work is done twice, gaps surface too late, and evidence is pieced together under pressure. The result:
- Unclear scope, negotiated during the assessment
- Evidence reconstructed after the fact
- Gaps discovered close to a deadline
- Policies that no longer match daily practice
- No owner once the review is over
The LABUSA Solution
Meet the obligation once, then keep meeting it.
LABUSA scopes each engagement to the obligation you actually face, not an entire framework. Your controls are assessed on evidence, every gap is recorded honestly, and fixes are planned in the order that matters most. LABUSA is certified to ISO/IEC 27001 itself, so these are requirements it operates under, not only advises on. Formal certification and independent audits are performed by an accredited third party.
-
Control Assessment
A structured review of controls, configuration and practice against a named standard or contract.
-
Framework Alignment
Gap analysis against NIST frameworks, CIS Controls and ISO/IEC 27001 readiness, as your obligations require.
-
Remediation Planning
Each gap described with what closing it involves, sequenced by risk and urgency.
-
Evidence Management
Practices and documentation that produce the record as a by-product of everyday work.
How LABUSA delivers
From strategy to ongoing support.
A typical engagement follows these stages, scoped to what you need.
-
Discovery & Assessment
Confirm the obligation and the scope it applies to, then assess each applicable control against evidence. -
Solution Design
Turn findings into a costed gap list and a remediation sequence leadership can approve and fund. -
Implementation
Where contracted, support remediation and update policies, procedures and evidence collection practices. -
Testing & Launch
Run a readiness review before the formal assessment, organize evidence and hand ownership to a named person.
The Results
Expected Business Outcomes
A clear, evidence-based approach to compliance helps you:
- Know exactly where you stand
- Plan and fund remediation with confidence
- Find gaps while there is time to close them
- Approach each review with evidence ready
- Keep controls owned after the assessment ends